阻止机器人表单垃圾与结账攻击在它们到达你的服务器之前。
机器人用垃圾条目轰炸您的潜在客户表单,用被盗信用卡测试您的支付处理器,并生成数千个虚假注册 — — 毒害您的 CRM 并危及 Stripe 账户被暂停。
Seatext 阻止机器人表单垃圾与服务器防护在 Cloudflare 边缘评估流量。只有当我们的引擎确认机器人的最终置信度分数达到 100 时,敏感请求才会被丢弃——保护你的源服务器、CRM 和结账流程,实现零误报。
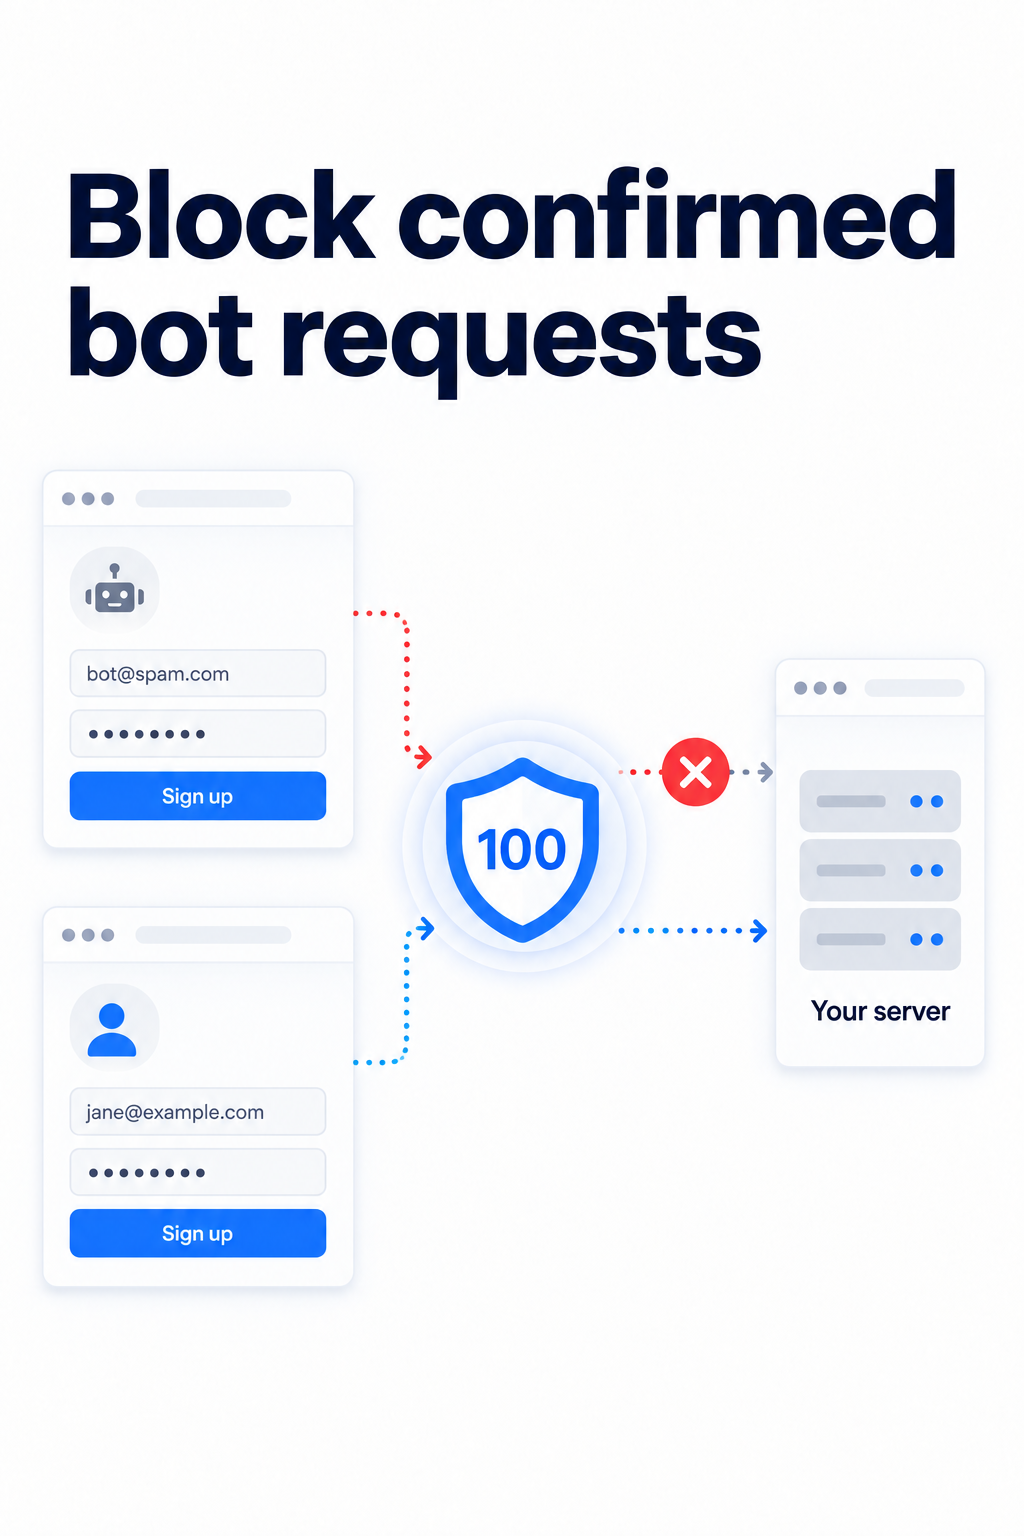
传统 WAF 和验证码为何失效
验证码会激怒真实人类买家并破坏结账转化率,而标准速率限制器会阻止合法的高级用户。Seatext 在边缘以 0ms 执行严格的 100 置信度生物特征检查,无摩擦。
Calculate how many origin requests & stolen leads Seatext prevents
当刮刮和凭证填充者轰炸您的端点时,源服务器浪费 CPU 循环,数据库充斥着垃圾用户注册,SDR 浪费数小时致电虚假号码。计算您的月度服务器和团队节省。
- Zero Customer Friction: No puzzles, warped text, or CAPTCHAs. Legitimate human shoppers experience instant, frictionless checkouts and form submissions.
- 100% Confidence Standard: Requests are dropped only when biometric, canvas, and network telemetry reaches an absolute 100-confidence threat score.
- Zero Origin Database Load: Fake signups and card testing scripts are blocked at the Cloudflare edge in 0ms, before reaching your backend.
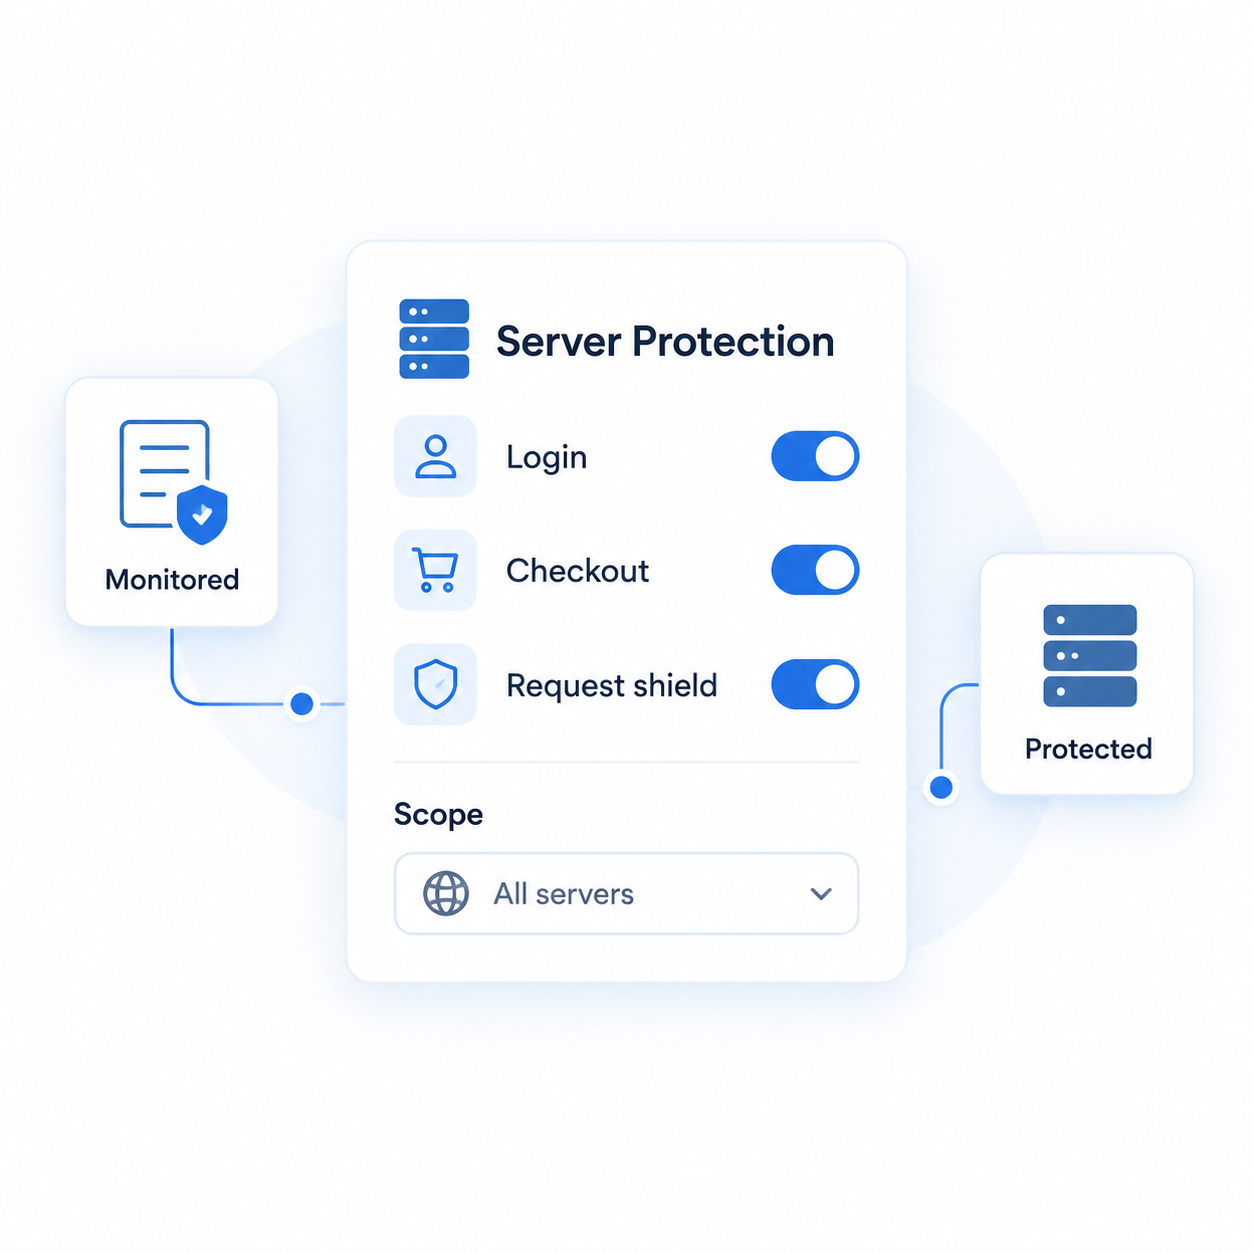
Precision protection for login, checkout, lead capture & reset endpoints
并非所有端点具有相同的业务风险。在您的 Seatext 仪表板中,为敏感交易流设置细粒度边缘策略,同时让无害的公共查询自由通过。
- Checkout & Card-Testing Defense: Blocks card testing bots using stolen credentials and coupon brute-force scripts before payment gateway charges.
- Credential Stuffing & Login Portals: Shuts down automated password spraying and brute force attacks on customer authentication routes.
- Lead Capture & Quote Forms: Stops junk registrations and spam submissions from polluting HubSpot, Salesforce, and outreach pipelines.
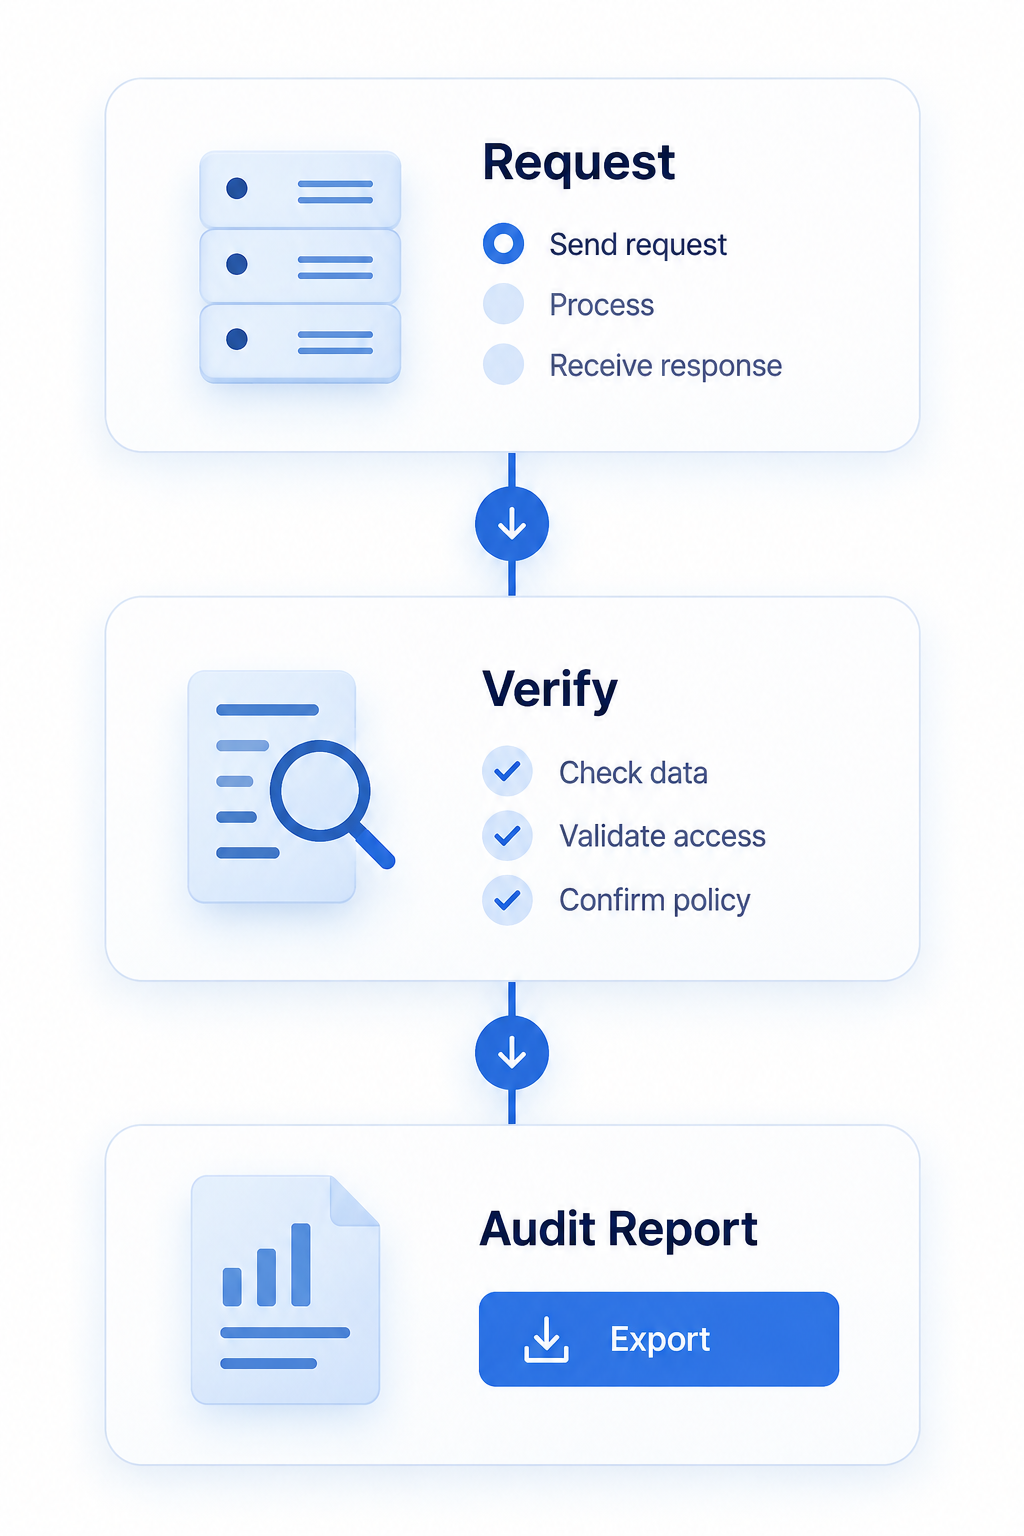
Complete audit trail with 0ms edge request verification timelines
每个被阻止的请求都被编译成一个法医审计档案,包含客户硬件指纹、IP 路由路径、击键动态和置信度日志 — — 可立即导出,用于安全合规和工程审查。
- Definitive Behavioral Proof: Comprehensive timeline logs documenting browser automation flags, canvas rendering anomalies, and execution timing.
- Autonomous Edge Termination: Drops malicious traffic with immediate HTTP 403 at Cloudflare edge nodes, consuming zero origin compute.
- One-Click Audit Dossier Export: Download formatted CSV and JSON reports to verify attack vectors with your DevOps and compliance teams.
四个关键端点全天候受保护
Seatext 防止脚本小子、无头浏览器和凭证填充者攻击您最有价值的转化流程。
Account Creation
Stops automated user registration, disposable email signups, and fake account floods from polluting your user database.
Authentication & Login
Protects customer login portals, password reset endpoints, and OAuth callback URLs from brute force and credential stuffing.
Checkout & Payments
Blocks card-testing bots using stolen credentials, coupon brute-force scripts, and automated checkout cart abandonment abuse.
Forms & Leads
Stops fake sales leads, quote requests, and consultation form spam from wasting your sales team's valuable calling time.
严格 100 置信度协议
永不丢弃合法客户。以下是我们的零误报系统如何保障收入。
1. Passive traffic observation
Seatext 在后台被动检查浏览器、硬件、画布和网络属性。普通访客体验即时页面加载,零摩擦。
2. 100% 置信度阈值
除非取证得分达到绝对 100,否则请求永不会被修改或质疑。任何边缘或模糊的流量将直接传递给人工流程。
3. 边缘级丢弃
一旦以 100% 置信度验证,敏感端点的 POST 提交将在边缘以 403 Forbidden 被拒绝,永不触及您的数据库。
Frequently asked questions
表单垃圾信息为何不仅仅是烦人的电子邮件?
Bot form submissions frequently trigger automated CRM email sequences, which leads to spam complaints, damaged domain sender reputation, and blacklisting by Gmail and Outlook. In addition, credit card testing on checkout pages can result in heavy per-transaction gateway penalties and merchant account termination from Stripe or PayPal.
Seatext 与 Google reCAPTCHA 或 Cloudflare Turnstile 有何不同?
Traditional CAPTCHAs introduce visual puzzles that frustrate users and decrease checkout conversion rates by 3% to 7%. Seatext works completely without visual challenges by evaluating deep client execution characteristics and drops bad actors at the edge before request execution.
这会破坏 API 集成或合法的第三方 Webhook 吗?
No. Server-to-server webhook endpoints (like Stripe webhooks, Zapier, or Salesforce syncs) can be whitelisted by route or header signature with zero interference.
